Ubuntu Accelerates Linux Kernel Security Updates in Response to AI Bug Reports
Canonical is shifting Ubuntu kernel updates to a 2-week SRU cycle published weekly, aiming to bring environments into a defensible, safer state within 24 to 48 hours of public disclosure.

Canonical announced that it is moving "from its current 4-week regular and 2-week security kernel Stable Release Update (SRU) cycles to a unified, rapid 2-week SRU cycle, published weekly."
The Dual Pressures: AI Scanning and Upstream CNA Changes
The shift is driven by an explosion in the volume of reported Common Vulnerabilities and Exposures (CVEs).
Canonical explained that the influx of vulnerabilities is "fueled by artificial intelligence: large language models (LLMs) and specialized AI agents have transformed bug discovery from a manual, time-intensive process into a highly automated engine."
At the same time, the upstream Linux kernel community became its own CVE Numbering Authority (CNA) and assigned identifiers to thousands of bugs, arguing that "at the kernel level, almost any type of bug that can affect a running system, could potentially be classified as a vulnerability."
Canonical notes that the volume of CVEs has "skyrocketed exponentially, creating a massive backlog of alerts and forcing defenders to drastically increase the speed of their fixes to close the window of risk."
How the Unified Two-Week Cadence Works
Under Ubuntu's current Kernel 4/2 SRU cycle, which concludes with the September 28 transition, Canonical maintains a 4-week standard stable update cycle plus "an additional planned update to be released at the 2-week midpoint of the following 4-week cycle." As detailed in the 2023 announcement, this midpoint update "will contain only CVE fixes rated critical or high and/or other time sensitive critical customer fixes that are deemed unlikely to cause regressions."
To manage the expanding vulnerability workload and speed up remediation, Canonical is transitioning to a unified two-week release cycle. As Canonical detailed on Ubuntu Discourse, "the exponential rise in vulnerabilities needing to be addressed in the Linux kernel has required us to accelerate our response accordingly."
According to the rollout schedule shared on Ubuntu Discourse, the transition begins with two back-to-back 2-week cycles starting September 28, 2026, and October 12, 2026, before the overlapping cycles begin on October 26, 2026. Once the overlapping cadence is active, fresh kernel releases will land weekly.
| Phase | Operations & Deliverables |
|---|---|
| Continuous Integration | Patch integration, snapshot of the tree at the cutoff date, and initial CI sanity checks. |
| Week 1: Prep (Builds & Smoke Tests) | Kernel preparation phase with builds and basic checks to confirm kernels boot and run with no obvious issues. Builds are published in -proposed. |
| Week 2: Cert (Extensive Testing) | Extensive certification, distro integration, and regression testing, with all test artifacts completed by the end of the stage. |
| Release | Kernels are released. |
Canonical noted that expedited releases are not possible while thoroughly testing every release candidate, stating: "We will retain extensive testing for each release, preserving the high degree of confidence the users of Ubuntu expect." Hardware validation remains a core component of this testing phase: "Through our Ubuntu Certified program, we rigorously test these kernels on different hardware types to ensure the best Ubuntu experience."
Fast-Tracking Fixes via the Proposed Pocket
For users "who are extremely sensitive to turnaround times" and have decided that "faster remediation is a higher priority than waiting for Canonical's extensive certification testing," Canonical provides an accelerated one-week pathway.
The -proposed archive pocket is where release candidates land after initial preparation. As Canonical points out, this "is where the kernel release candidates are published prior to starting certification testing and therefore updated weekly as part of the overlapping SRU cycles," allowing administrators to run their own acceptance testing early.
Guidance on enabling -proposed and testing packages is available in Enable proposed - Ubuntu project documentation.
Rapid Interim Mitigations Within 24 to 48 Hours
While a patch is being prepared, Canonical "aims to provide safe workarounds where applicable, so users aren't left exposed in the meantime." When no safe workaround exists, "Canonical will say so clearly and point users toward general hardening steps instead."
The stated objective is to "get environments into a defensible, safer state within 24 to 48 hours of public disclosure", well before a patch ships. As Canonical emphasizes, interim guidance "doesn't replace the patch; it buys the time needed to fix the vulnerability properly, without sacrificing security."
Sources & References
- Canonical: Accelerating delivery of CVE fixes with a new Kernel release strategy (Published September 23, 2026)
- Ubuntu Discourse: Going from 4 to 2, accelerating the Linux kernel release process (Published September 24, 2026)
- Ubuntu Discourse: Ubuntu Kernel 4/2 SRU Cycle Announcement (Published August 1, 2023)
- GamingOnLinux: Ubuntu to get quicker Linux kernel security updates due to so many AI reports (Published September 24, 2026)
- Ubuntu: Certified hardware (Accessed September 24, 2026)
- Ubuntu Documentation: Enable proposed - Ubuntu project documentation (Accessed September 24, 2026)
More from the desk
AMD to Acquire AI Inference Silicon Startup Taalas
AMD agrees to acquire Toronto startup Taalas to embed hardwired AI models directly onto silicon, tackling energy and latency bottlenecks in inference workloads.
Nobody Is Always Cheapest: What 33,000 Grocery Prices Taught Us About India's Grocery App Price War
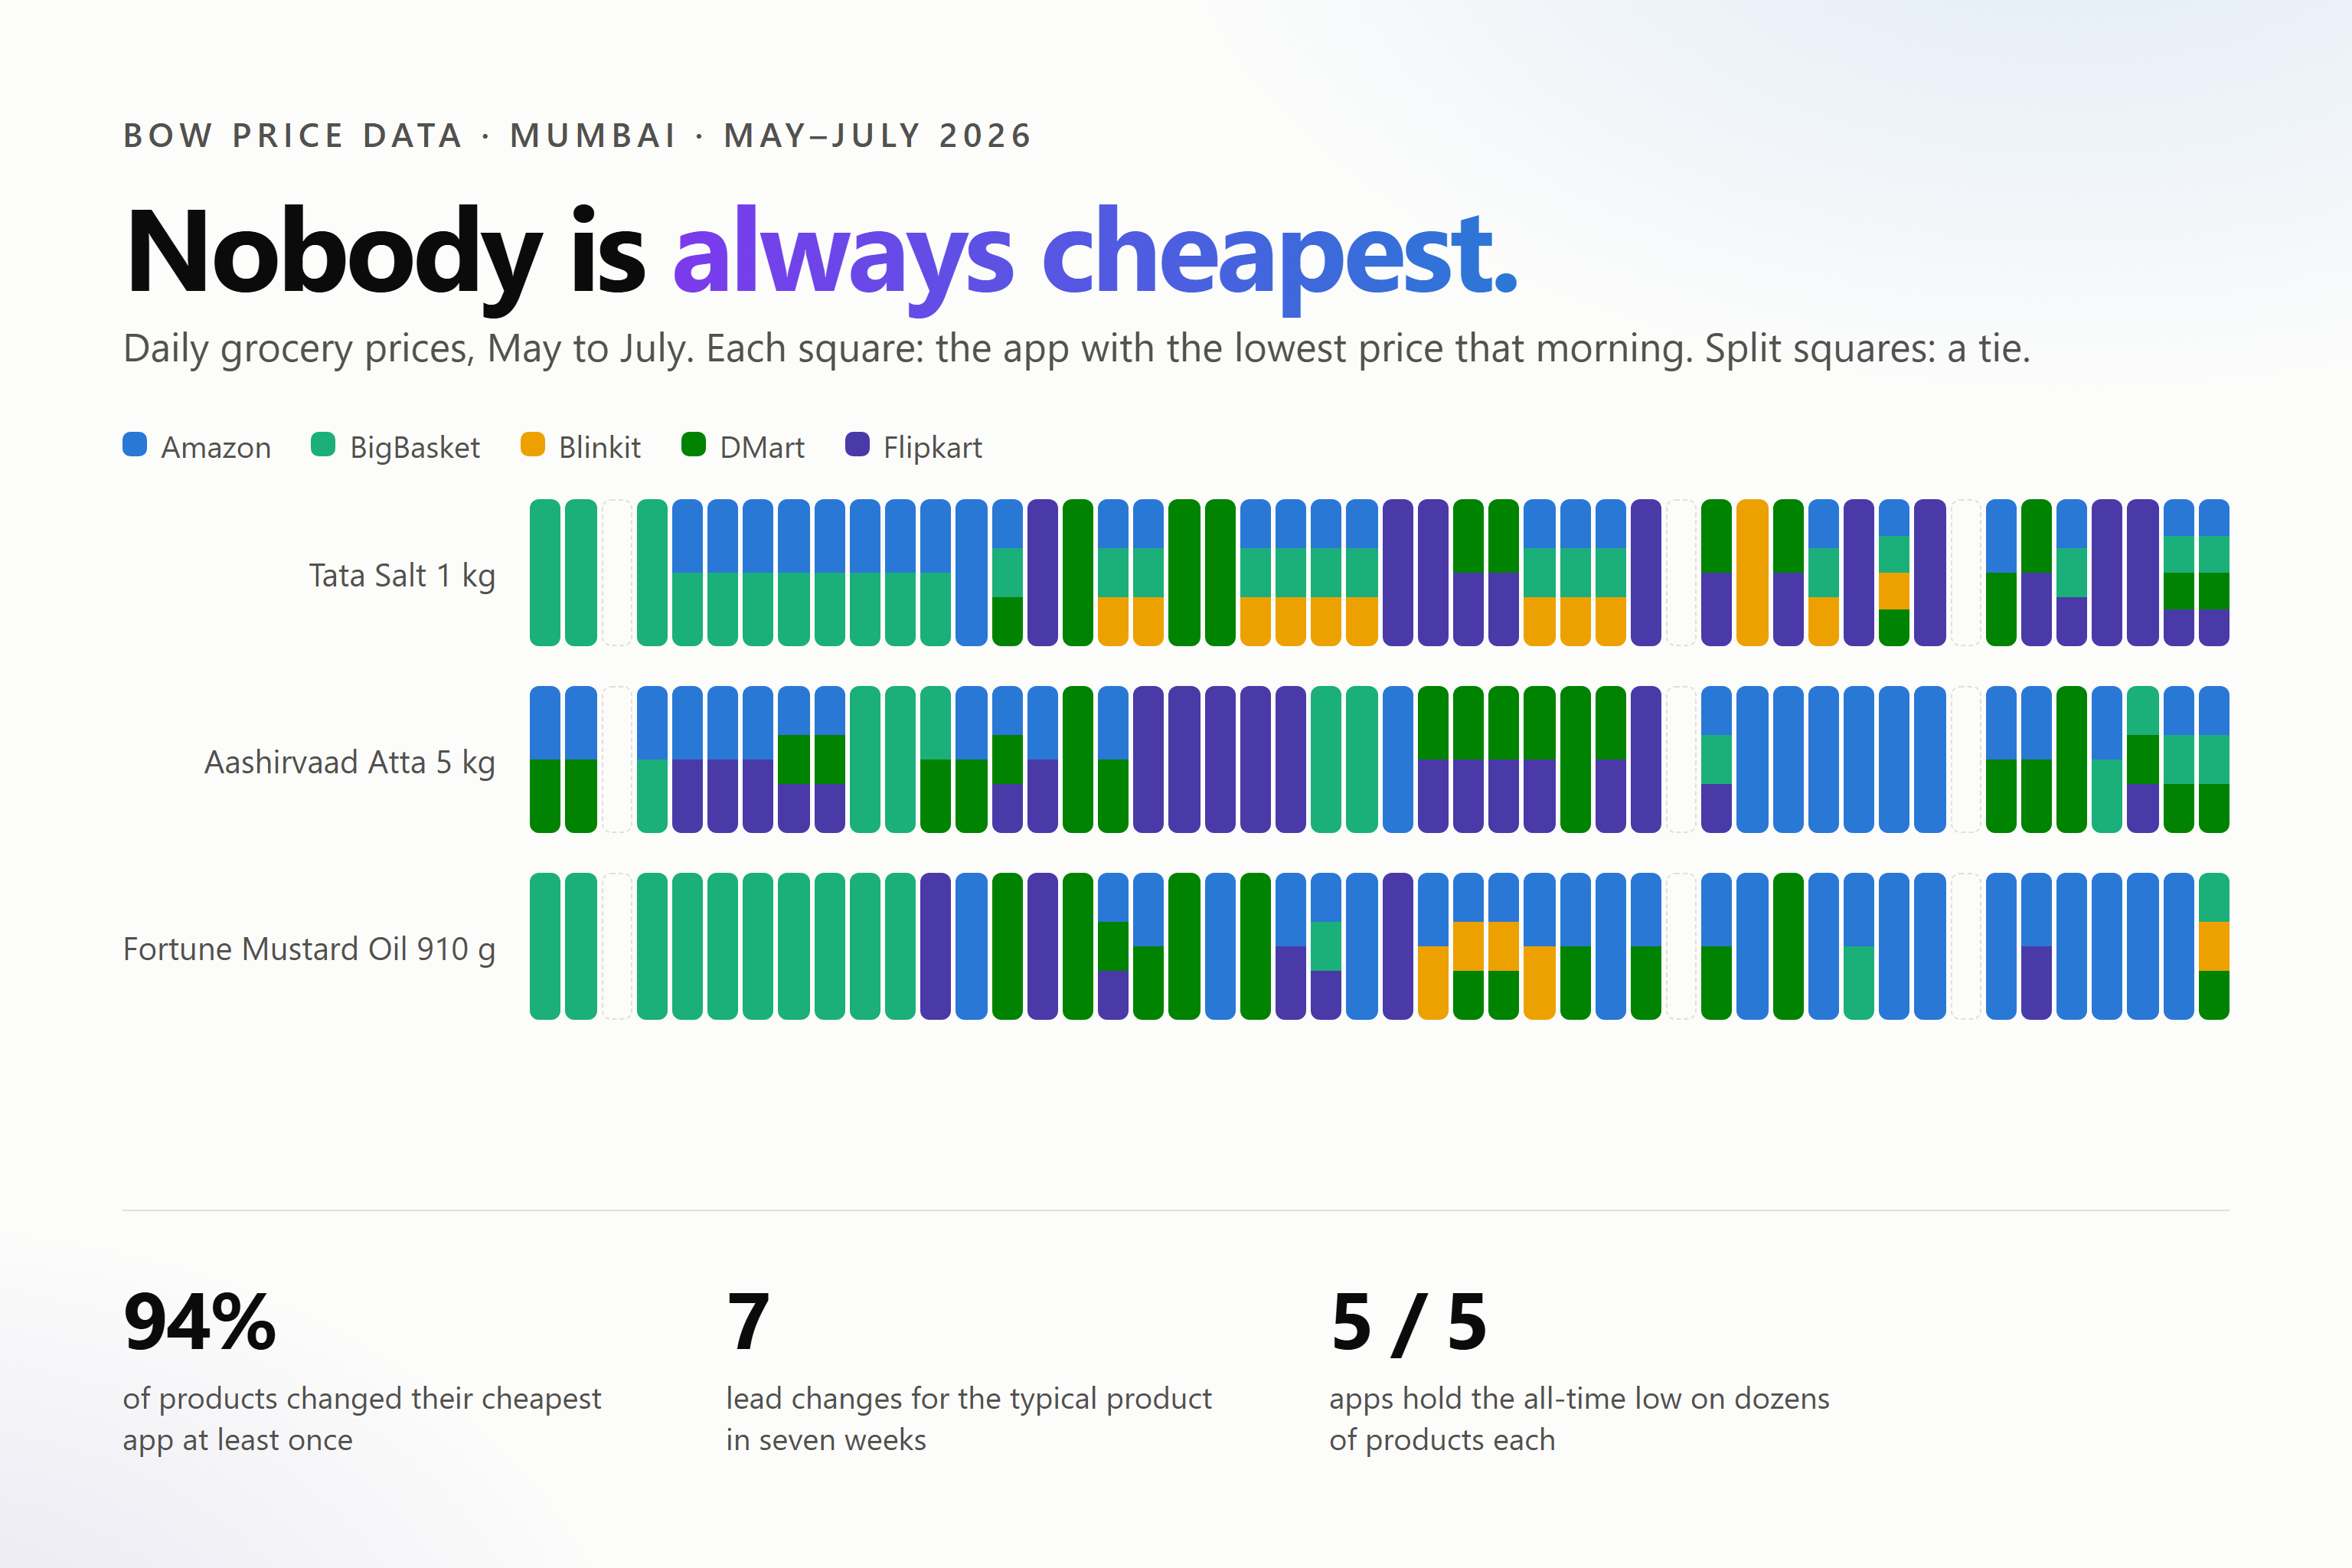
Seven weeks of daily price data from BOW, across DMart, BigBasket, Blinkit, Amazon and Flipkart in Mumbai. The verdict: 94% of products changed their cheapest app at least once, every platform holds all-time lows, and the real money is in timing, not loyalty.
Siri AI, iOS 27, and the End of an Era: Everything Announced at Apple's WWDC 2026
Apple's WWDC 2026 delivered an AI-centric keynote featuring a Siri overhaul collaborating with Google Gemini, the release of iOS 27 and macOS 27 Golden Gate, and a historic leadership transition as Tim Cook prepares to step down.